
Every litre accounted.
Every action verified.
AID-Fuel is an end-to-end fuel automation system that replaces paper-based registers with a secure, wireless, tamper-proof digital ecosystem — from sensors and dispensing units to command-level dashboards. No manual data entry, no proprietary lock-in.
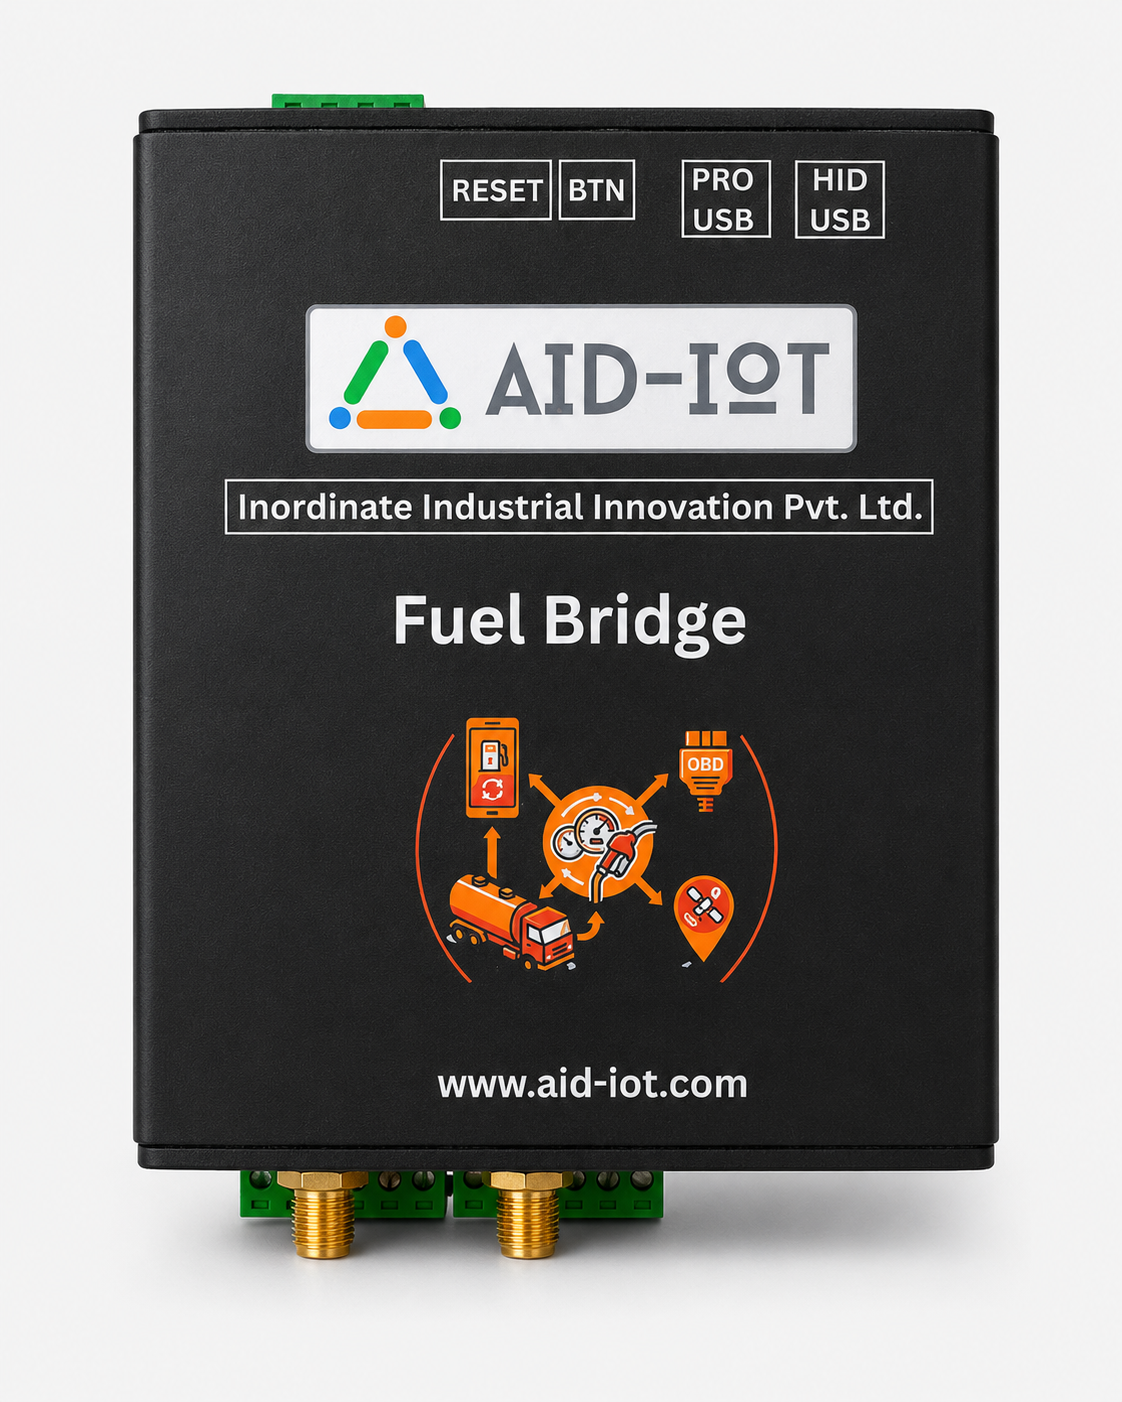
The Problem
Fuel management still runs on paper and goodwill.
Across depots, fleets, and dispatch sites — registers are filled by hand, vendors are siloed, and HQ sees yesterday's numbers. AID-Fuel rebuilds the chain end-to-end.
TODAY · CONVENTIONAL
Stale data, manual reconciliation, no audit trail.
- Manual data entry into registers and spreadsheets — prone to error and manipulation
- Heterogeneous ground hardware (ATGs, DUs, flow meters) with no unified data collection
- No real-time visibility — HQ works with stale, manually compiled data
- Reconciliation is complex, time-consuming, unreliable without a single source of truth
- No tamper-proof audit trail — critical for accountability and compliance
- Sites operate in silos — no federated, real-time command picture
WITH AID-FUEL
Sensor-direct, cryptographically signed, command-ready.
- Direct hardware integration — data flows from sensors, never from a keyboard
- NavIC time synchronisation — every transaction is satellite-authenticated
- Wireless backhaul — no fibre, no LAN, no civil works between sites and server
- Cryptographic signing of every record — tamper-proof by design
- Works in isolation when the network is down; auto-syncs on reconnect
- Federated, real-time command dashboards across every site
System Architecture
Five layers, ground to command — pull-only.
A strict ground-to-HQ pull-only data flow over a sovereign wireless network — no public internet exposure, and no unsolicited outbound data from field devices.
LAYER 1
Ground Hardware
LAYER 2
EDGE Device
LAYER 3
Wireless Backhaul
LAYER 4
FIRST Server
LAYER 5
Application Suite
LAYER 1
Ground Hardware
ATGs, dispensing units, flow meters, hydrant panels. RS-485 with dual galvanic isolation. Hardware-neutral — onboards any vendor's digital output.
LAYER 2
EDGE Device
Purpose-built FreeRTOS computing node. Signed firmware only. Local cache of 1,000 transactions. Tamper detection. Constraint-locked by design.
LAYER 3
Wireless Backhaul
Encrypted cellular VPN over a sovereign private network. No fibre, no LAN, no public internet. Multi-band modem auto-selects the best link.
LAYER 4
FIRST Server
Centralised Spring Boot + MongoDB application. Pull-only ingress, JWT/OAuth2 auth, AES-256 at rest, SHA-256 firmware validation, 5-yr immutable logs.
LAYER 5
Application Suite
FSMS command dashboard, DEPOT desktop, RAVEN field client, QUEST indent web — role-aware, signed-token authenticated.
NavIC Integration
Authentic time, cryptographically bound to every litre.
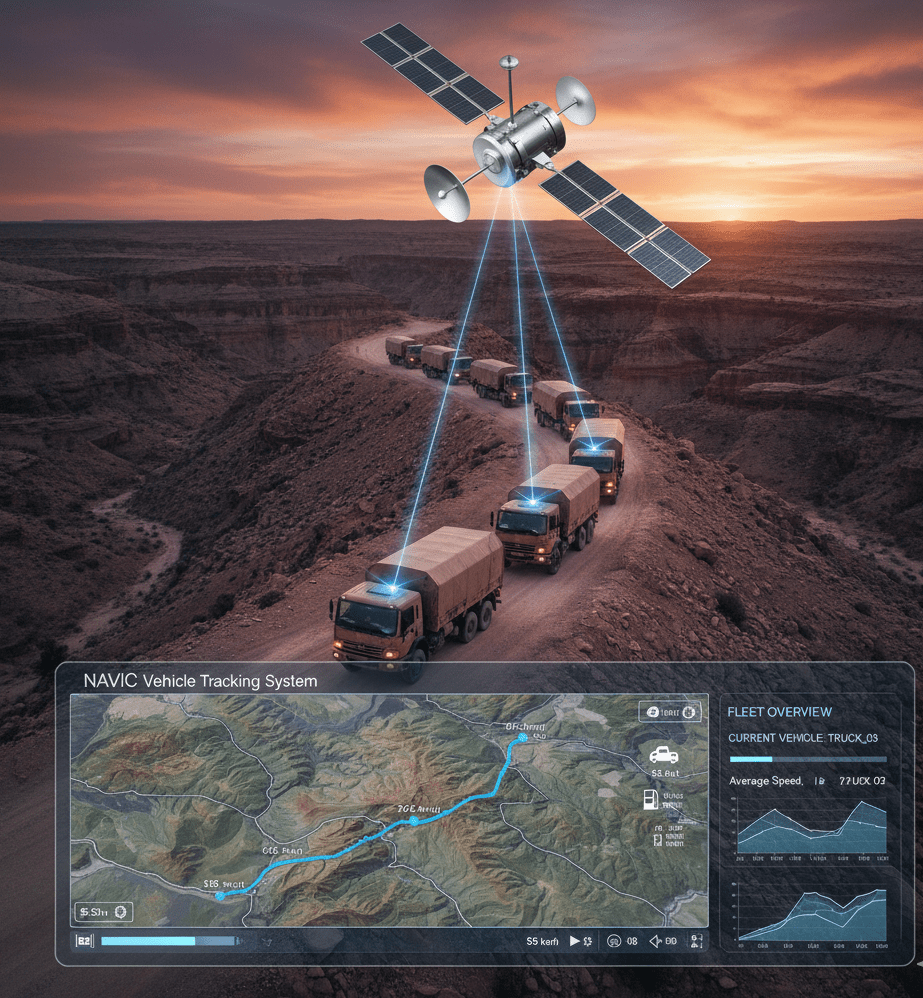
Every fuel event carries a NavIC-authenticated timestamp that cannot be spoofed, backdated, or manipulated. Time is sourced externally — not from the device clock.
How NavIC time sync works
- 1
A NavIC-compatible receiver module on the EDGE device locks onto the constellation.
- 2
The receiver delivers a 1-PPS signal and authenticated NMEA time stream to firmware.
- 3
Every transaction is timestamped using NavIC time — not the device's local clock.
- 4
The NavIC timestamp is cryptographically bound to the transaction before upload.
- 5
On signal loss, a disciplined oscillator holds time accuracy through the gap.
Sovereign
Operates entirely under Indian control with no dependency on foreign satellite systems.
Authenticated signals
Encrypted and authenticated — harder to spoof than civilian GPS.
Dual-frequency
L5 + S-band operation delivers higher accuracy and integrity for the Indian subcontinent.
Authenticated 1-PPS
Receivers deliver an authenticated pulse-per-second directly to EDGE firmware.
WHY IT MATTERS · AUDIT & ACCOUNTABILITY
Tamper-proof chronology that holds up in any audit.
Immutable chronology
No operator can alter the time of a dispensing event after the fact.
Evidence-grade records
NavIC + signature + immutable storage meets the highest evidentiary standards.
Cross-site correlation
HQ compares events across sites on one trusted time reference.
Replay-proof
Signed, time-bound tokens can't be replayed to issue fuel twice.
Security Architecture
Five layers of defence. No bolt-ons. Structural.
Security is not an add-on — it is built into the data flow, hardware, software, and physical handling of every component.
01 · DATA FLOW
Pull-only, sovereign backhaul
- Server initiates all pulls — EDGE cannot push unsolicited data
- Encrypted cellular VPN over a sovereign private network
- Field zone and HQ zone fully segregated — no cross-zone traffic
- TLS 1.3 end-to-end. No plaintext at any hop.
02 · HARDWARE
EDGE device hardening
- Signed FreeRTOS image — unsigned firmware cannot boot
- Watchdog timer + MPU prevents runaway processes
- Dual RS-485 galvanic isolation blocks signal injection
- Voltage rail + enclosure breach sensors log tamper events
03 · APPLICATION
Identity, signatures, sessions
- RBAC with non-overlapping privilege sets per role
- Every transaction signed with private key on device or server
- Signatures bind the NavIC timestamp — no time manipulation
- Critical operations require re-authentication
04 · DATA
Encryption & integrity
- AES-256 at rest, SHA-256 firmware & log integrity checks
- MongoDB write-once collections, 5+ year retention
- Periodic secure backup to designated archive
- Encrypted local cache verified before clearing
05 · PHYSICAL
Operational controls
- Server under supervised access — no unauthorised entry
- EDGE enclosures with tamper seals and QR access logs
- Firmware updates only via signed OTA from the server
- Field devices in a separate physical zone from HQ
Constraint Node Design
A general-purpose computer is a liability. A constraint node is inert.
The EDGE device is purpose-locked at hardware, firmware, and network levels — it can perform exactly one mission and nothing else. This is not a software policy. It is structural.
Hardware level
- JTAG, USB host, and debug interfaces physically disabled at manufacture
- Radio locked to communicate only with its registered server over an encrypted VPN
- Device identity & root-of-trust keys live in OTP memory — unalterable
Firmware level
- Signed image validated on every boot — modified images do not boot
- Single-function task scheduler — no additional tasks can be added
- No CLI, no shell, no interactive session — ever
Network level
- Hardware-ID whitelisting — server only accepts registered devices
- Pinned TLS certificate — device cannot connect to any other host
- Data volume limits — anomalies alert HQ immediately
CONSEQUENCES — LOSS, THEFT, AND UNATTENDED OPERATION
What happens when things go wrong
Device is lost
Hardware ID revoked at server. Cannot authenticate anywhere. Storage is AES-256 — useless without the key.
Device is stolen
ID revoked the moment theft is reported. Pinned cert prevents connection to any other server. Operationally inert.
Left unattended
Normal and intended — designed to run sensor→encrypt→cache→sync continuously, no human required.
Examined by adversary
Firmware signed and encrypted, keys in OTP memory, credentials pinned to a revoked server. No extractable secrets.
Firmware tampered
Signed boot validation refuses to execute. Device halts safely and logs the event to the tamper record.
Application Suite
Four applications, one signed-token identity.
Every client app authenticates against the central server with the same JWT / OAuth2 identity — so roles, audit trails, and signatures are consistent end-to-end.
FSMS
Web Browser
Central command dashboard.
- Live monitoring across sites
- Anomaly alerts
- Reporting & reconciliation
DEPOT
Desktop · Electron
Outbound and inbound fuel movement.
- Receipt and issue
- Tank reconciliation
- Gate management
RAVEN
Desktop · Electron
Field operations with offline sync.
- Real-time field transactions
- Offline-first cache
- Auto sync on reconnect
QUEST
Web Browser
Indent and approval workflow.
- Indent creation
- Multi-level approval
- Drawal tracking
Unique Strengths
Ten reasons AID-Fuel is structurally different.
Every architectural choice — from the wireless backhaul to NavIC time sync to the constraint-locked EDGE — flows from one principle: trust nothing that has not been cryptographically verified.
Zero manual data entry
Every record originates from certified ground hardware — never from a keyboard.
NavIC time integrity
Satellite-authenticated timestamps on every transaction.
Hardware neutral
Speaks RS-485/Ethernet to any vendor's existing hardware — no CapEx wastage.
Wireless, no cabling
Encrypted cellular backhaul between EDGE and server — no fibre, no LAN, no civil works.
Rapid expansion
A new site is live within hours — place the EDGE, provision once, done.
Offline resilient
1,000-transaction local cache; auto-syncs on reconnect — zero data loss on outage.
Constraint node EDGE
Purpose-locked hardware — inert if lost or stolen, safe to deploy unattended.
Sovereign network
Multi-band modem supports all major bands; runs on isolated private cellular.
100% indigenous
Designed, developed, and manufactured in India — hardware, firmware, and software.
5-year audit trail
Immutable, AES-256 encrypted, cryptographically signed logs in MongoDB.
THE GOVERNING PRINCIPLE
Trust nothing that has not been cryptographically verified. Depend on nothing that is not indigenously controlled.
From the RS-485 sensor connection to the wireless uplink to the command dashboard — every layer is sovereign, NavIC-authenticated, and built to expand to a new site in hours.
Have a problem?
We design, deploy, and scale the
solution.
